One click – and your patient data is in someone else’s hands.
Health data cannot be recalled and cannot be reissued. That is why practices are a favourite target, and why your team needs a reliable instinct for that one fake email, even on a packed day. That is exactly what I train – no IT department needed, no jargon, in about 45 minutes per person.
Training, phishing test, six months of refreshers and proof of training. No subscription. A practice with six people pays €294 net.
Online, can be paused at any time, even in short stages between two patients. Your own effort: enter your team, done.
Who was trained and when, plus the team rate. Exactly what the KBV guideline means by “verifying participation”.
All I need is the name and email address of your staff. The TI connector, KIM (the secure healthcare email service) and practice management software remain untouched.
What criminals do with patient data – and what it costs you.
You can hardly put a figure on the value of your data, but the attackers can. Patient data is not “stolen”, it is copied: you still have it, and now someone else does too.
With diagnoses, findings or treatment histories in hand, criminals write to the patients themselves: pay or it gets published. At the Finnish psychotherapy provider Vastaamo, this affected tens of thousands of patients.
If no ransom is paid, lab results, doctors’ letters and addresses end up openly online, as happened in 2025 after the attack on the LUP hospitals in Mecklenburg-Western Pomerania. There is no getting them back.
Insurance number, date of birth and address are enough for fraud in your patients’ names: prescriptions, orders, accounts. Suspicion falls first on the practice the data came from.
Encrypted systems mean no access to records, appointments and billing, often for days. Recovery, forensics and legal advice usually cost far more than any ransom.
And this is what you then have to do
Notify the state data protection authority as soon as a risk to those affected cannot be ruled out (Art. 33 GDPR).
Inform every affected patient if the risk is high, which with health data is practically always the case (Art. 34 GDPR).
Responsibility for medical confidentiality (§ 203 StGB) and possible fines and damages; lost trust in your community cannot be insured.
Almost every one of these cases starts with an email that one person believed was genuine. Recognising that one email is what I train.
This is how your sector is being attacked right now.
I recreate these scenarios in realistic simulations, so your team recognises them when it counts instead of only understanding them after the damage is done.
An alleged fee notice or billing error pushes staff to log in on a copycat website.
An email demands an “urgent update” of the connector, including login details.
An alleged patient request brings a malicious file into the practice – a gateway for ransomware.
A supposed message from the secure network leads to a fake login page.
What you have to do – and what this lets you tick off.
For practices, what counts is the IT security guideline of the KBV (National Association of Statutory Health Insurance Physicians) under § 390 SGB V (German Social Code, Book V; until 2025: § 75b) and the GDPR. The guideline was revised in April 2025, and its training requirements have applied to practices of every size since 1 October 2025. Each point states openly whether I cover it, partly support it or whether it lies with your IT – linked to the matching attack scenario.
The course is exactly the required “training dedicated to IT security and data protection”. The KBV explicitly names e-learning as an easy-access route. Participation and date are recorded in the proof of training.
Passwords and two-factor authentication, checking senders and attachments, the call-back rule and the reporting channel each have their own chapter in the course.
You take the same course as your team and see in the Cockpit where the practice stands. The proof of training documents both.
The phishing test after the training shows whether this sticks in everyday work, with TI, KIM and KV-related themes.
You add new colleagues with one click and they start with the same knowledge. The formal confidentiality undertaking and the return of access credentials remain your responsibility.
The KBV guideline specifies the state of the art under Art. 32. Trained staff are the organisational part; your IT service provider adds the technical side.
The course practises the internal reporting channel: who calls whom, what gets noted down, what not to do. The report itself and the breach register are handled by you or your data protection officer.
Not part of awareness training – this lies with you or your IT service provider.
The KBV does not certify practices and does not carry out active checks; the guideline is a minimum standard and becomes the benchmark in the event of damage and when the data protection authority makes enquiries. What the KBV additionally requires of large practices, namely measuring learning success (Annex 3 No. 1), you get from me anyway: quiz and team rate.
This is what you have in hand after the run.
You write none of it yourself. Once the last person in your team has finished, everything is in the Cockpit; you download it and file it with your practice records.
Who was trained and when, the team rate from the phishing test, timestamp. The document the authority wants to see.
🔎 Certificate for each person, verifiableEvery employee receives a certificate of participation whose authenticity anyone can check online.
🔒 Data processing agreement (DPA)I process the names and email addresses of your staff. The agreement for this is concluded on registration, as a PDF for your data protection records.
This is what it looks like in practice.
Cockpit, team report, certificate and proof of training for a fictitious company with twelve people. All names and results are made up; the layout is exactly what you will see yourself later.
Groups, registered people and the cost if everyone completes. From here you start training, an initial test or a repeat run.
The team’s click and data-entry rates, a comparison with all test runs, participation in training. Anonymised.
Results at a glance and protection level with a recommendation. The PDF carries an authenticity QR code and is suitable for audits, insurers and NIS2 documentation.
Name, course, dates of training and practical test, reference to standards, signature and a verifiable certificate number with QR code.
All training carried out, with time stamps and participation rates, mapped to the requirements. Also for ISO 27001, GDPR, the AI Act and cyber insurance.
Each person sees only their own result: reaction to each test email, how the scam could have been spotted, and what their device gave away.
This is how my training works.
Your day-to-day practice leaves no time for training projects. So the training adapts to you: from reception to treatment room, everyone learns the same basics, each person whenever there is a quiet moment, without the practice grinding to a halt.
Two ways – you choose what suits you.
I train your team in person – on site or online, in conversation and with examples from your everyday work.
Everyone learns online the way they prefer – by text or video, at their own pace, choosing the content.
Train first, then test – deliberately in that order.
-
Initial training
First I equip your team (or you do it with my materials). Everyone starts with the same basic knowledge.
-
Phishing test as a self-check
Only then does the simulated attack follow – not as an exam, but as a self-check: everyone sees whether what they learned holds up in everyday work.
-
A security culture, refreshed when needed
Training and testing grow into a constructive security culture in your business, which you simply repeat when the time comes.
Your status report is based on your team’s results after the training – it shows the level you set out to reach, not the unprotected starting point.
The reverse order, testing first and training afterwards, is technically possible. Especially in a practice where everyone works under time pressure, a test “in at the deep end” can strain trust: anyone who falls for a fake KV or TI email without training quickly feels exposed rather than empowered.
No subscription, as and when you need it, and always with my personal support.
A contact person from southern Baden, not a hotline.
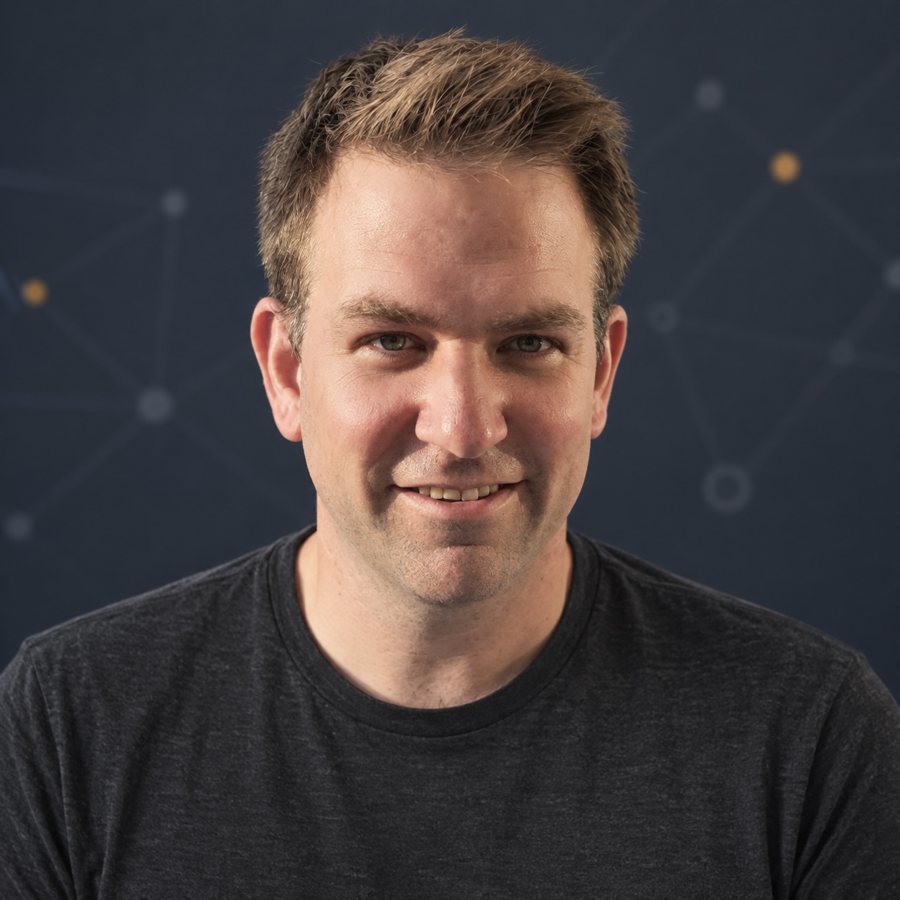
I am Patrick Ihle, founder of secureIT. Professionally I work in information security, and for more than 20 years I have also been a trainer and lecturer alongside my job. secureIT is my own business in Ballrechten-Dottingen near Freiburg. I visit practices in southern Baden in person on request and support everyone else online. You write to me, and I answer myself.
More about mePatient data does not belong in any AI tool.
Rephrasing a doctor’s letter, translating a finding, answering a patient enquiry: AI is quick to hand in a practice. With patient data, this becomes a disclosure of health data to an outside provider, with consequences under the GDPR and medical confidentiality. Since February 2025 you are also required to train your team in AI literacy.
- Health data enjoys special protection (Art. 9 GDPR), and medical confidentiality also applies to AI providers (§ 203 StGB, German Criminal Code)
- Training obligation for everyone who uses AI (Art. 4 EU AI Act)
- My AI course with a certificate for each person and a template AI policy for the practice
For your practice.
The full comparison with the GDPR, cyber insurance and ISO 27001, in case your insurer or your network asks for more.
Free self-test →Three simulated phishing emails to your own address. This lets you see in advance what the test for your team looks like.
About me →Background, approach and why I offer phishing training as a one-person business.
Frequently asked questions
Is this enough for the KBV IT security guideline?
Does the phishing simulation touch my TI, KIM or practice software?
How much time does this really take my team?
Do I have to tell my employees about the phishing test beforehand?
What happens to my employees’ data?
Is this a subscription?
What does it cost?
Does the effect of a one-off training actually last?
Do I need an IT department for this?
How does training with you work?
Will anyone on our team be singled out or monitored?
Does this cover GDPR, NIS2, ISO 27001 or insurance requirements?
What happens when staff change?
Do I get proof of training or a certificate?
Does this also cover AI fraud and deepfakes?
Are schools and non-profit associations really free of charge?
How quickly can I start?
Your question is not listed?
Ask me directly. You only need to give an email address if you want to receive my answer.
Set up in an hour, trained by Friday.
Enter your team, activate the course, done. The proof of training for the KBV guideline is created automatically. The account is free; you only pay when you start.