The one line in the cyber insurance questionnaire that costs prospects money and scares them off. And how to solve it.
“Are all employees regularly trained on phishing, and is this documented?” If your client ticks no, the result is a rejection, a surcharge or an exclusion. You give them a link, I deliver training, test and proof. You get 20 % on every invoice, including the repeat in the following year.
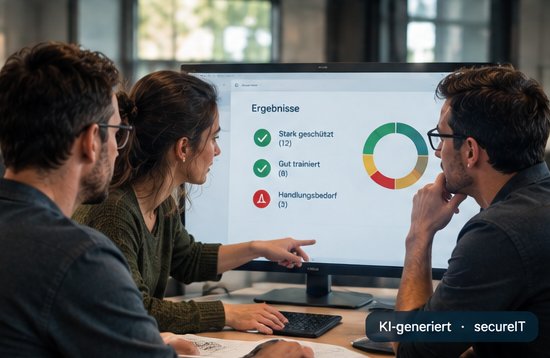
What the proof ticks off in the questionnaire.
Questions along these lines appear at Hiscox, HDI, AXA and Allianz. After the run, your client answers them with yes, and the evidence is attached.
| Question in the questionnaire | Your answer after the programme | Evidence |
|---|---|---|
| Regular employee training on phishing? | Yes, repeated annually. | Certificate for each person |
| Documentation with participants and date? | Yes, with a timestamp. | Evidence sheet for each business |
| Phishing simulation with evaluation? | Yes, after the training. | Team report |
| Can the proof be verified? | Yes, by number and QR code. | Online authenticity check |
The proof does not cover technical questions (MFA, backups, patches). It says so on the proof itself, so the underwriter does not read anything into it that is not there.
The email to your client, already written.
Copy it, replace the placeholders, insert your partner link. That is all.
Subject: Training proof for your cyber insurance

Dear MS/MR NAME,

The risk questionnaire for your cyber policy asks whether your employees have received documented phishing training. Without this proof, you risk a premium surcharge or the exclusion of social engineering losses.

A lean solution for this is secureIT: online training, phishing test and verifiable certificate in one run, €49 per person one-off, no subscription, set up in ten minutes. For your team, it is done in about a week.

You can start right here: YOUR-PARTNER-LINK

Just send me the proof afterwards and I will submit it to the insurer.

Kind regards
YOUR NAME
This is what it looks like in practice.
Cockpit, team report, certificate and proof of training for a fictitious company with twelve people. All names and results are made up; the layout is exactly what you will see yourself later.
Groups, registered people and the cost if everyone completes. From here you start training, an initial test or a repeat run.
The team’s click and data-entry rates, a comparison with all test runs, participation in training. Anonymised.
Results at a glance and protection level with a recommendation. The PDF carries an authenticity QR code and is suitable for audits, insurers and NIS2 documentation.
Name, course, dates of training and practical test, reference to standards, signature and a verifiable certificate number with QR code.
All training carried out, with time stamps and participation rates, mapped to the requirements. Also for ISO 27001, GDPR, the AI Act and cyber insurance.
Each person sees only their own result: reaction to each test email, how the scam could have been spotted, and what their device gave away.
This is how my training works.
You register once as a partner and receive a link. You send it to your client when the questionnaire is on the table. The client buys directly at the list price, and I take care of training, test and proof. With the business’s consent, you receive the proof directly.
Three ways – you choose what suits you.
I train your team in person – on site or online, in conversation and with examples from your everyday work.
You run the training yourself: I provide the ready-made materials and you pass them on in-house – at your own pace.
Everyone learns online the way they prefer – by text or video, at their own pace, choosing the content.
Train first, then test – deliberately in that order.
-
Initial training
First I equip your team (or you do it with my materials). Everyone starts with the same basic knowledge.
-
Phishing test as a self-check
Only then does the simulated attack follow – not as an exam, but as a self-check: everyone sees whether what they learned holds up in everyday work.
-
A security culture, refreshed when needed
Training and testing grow into a constructive security culture in your business, which you simply repeat when the time comes.
Your status report is based on your team’s results after the training – it shows the level you set out to reach, not the unprotected starting point.
New team members can be added later with one click: they immediately receive the online training materials and a first self-test – and join the next joint session or training with the same prior knowledge.
The reverse order – and why I advise against it.
From a management perspective, it often seems logical to assess the situation with a test first and only then decide whether training is needed. Technically that works – I can set it up for you.
Some businesses just want a quick phishing test “for the insurer”. But that does not produce proof of training, and that is exactly what the questionnaire asks for. Training first, then testing delivers both. A test without prior training only measures the starting point at zero. My approach turns this around: equip first, then check.
No subscription, as and when you need it, and always with my personal support.
AI is the next topic in your clients’ risk questionnaires.
Deepfake calls from the “boss”, flawless fraud emails, employees pasting customer data into chatbots: AI is changing your clients’ cyber risk. Since February 2025, businesses that use AI have to train their staff. My AI course with proof of training fits into any conversation about cyber risk, and the partner commission applies to it as well.
- AI-assisted fraud: deepfakes, voice clones, CEO fraud
- AI literacy obligation under Art. 4 EU AI Act, with a certificate for each person
- As a bundle with the phishing training, commission as usual
For your decision.
20 % on the first and follow-up purchases, credited when payment is received, paid out from €50.
Proof page for your clients →The page you can send your client instead of a long explanation.
Verify a certificate →This is the authenticity check the underwriter can carry out themselves.
Frequently asked questions
As a broker, do I have to set anything up or train anyone myself?
How high is the commission, and when is it paid?
Can the underwriter verify the certificate themselves?
Is this a subscription?
What does it cost?
Does the effect of a one-off training actually last?
Do I need an IT department for this?
How does training with you work?
Will anyone on our team be singled out or monitored?
Does this cover GDPR, NIS2, ISO 27001 or insurance requirements?
What happens when staff change?
Do I get proof of training or a certificate?
Does this also cover AI fraud and deepfakes?
Are schools and non-profit associations really free of charge?
How quickly can I start?
Your question is not listed?
Ask me directly. You only need to give an email address if you want to receive my answer.
Register, copy the link, send it with the next questionnaire.
No minimum volume, no training for you, no fee. Just the commission.